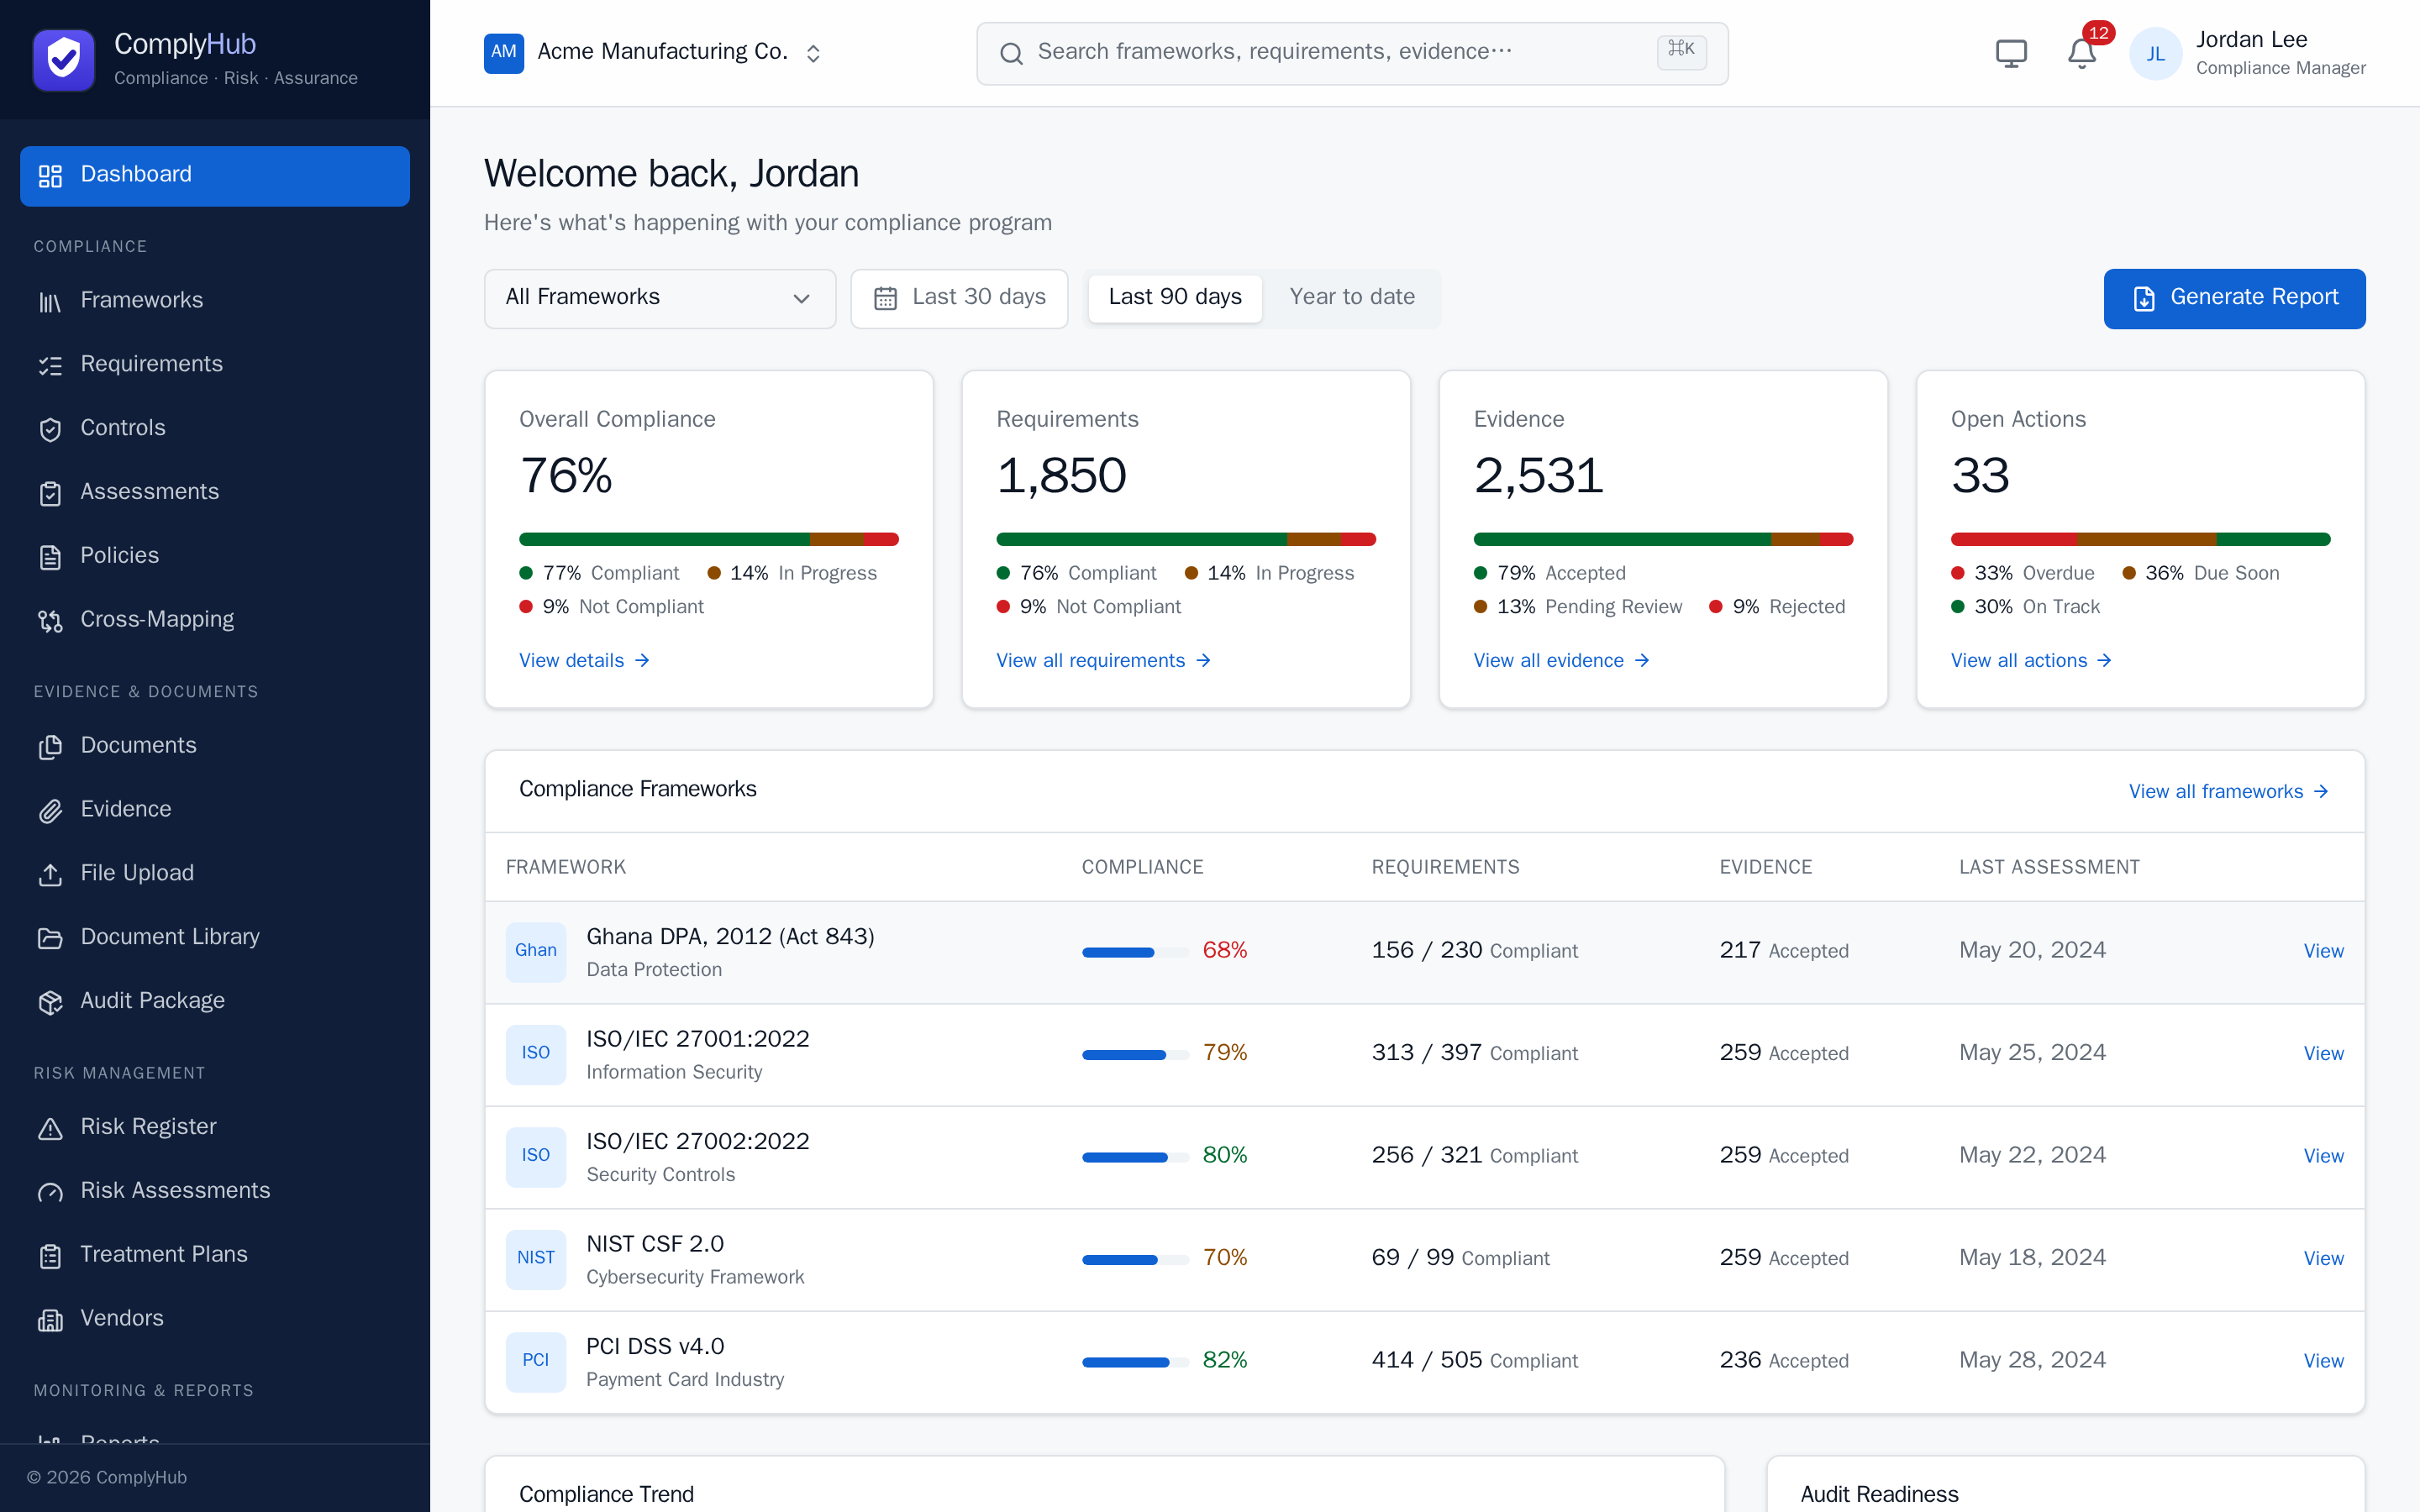
Frameworks supported out of the box
How it works
From adopted framework to audit-ready, in three steps
Adopt a framework
Pick the regime you need to comply with. Requirements populate automatically as a master checklist scoped to your organization.
Assign owners, attach evidence
Controls satisfy requirements; evidence proves the controls work. Both carry an owner and a review lifecycle from day one.
Watch your readiness score climb
One composite number tells you exactly how close you are to audit-ready — then hand auditors a package with one click.
Everything connected
A GRC program needs more than a checklist — here's the whole thing
Not a pile of disconnected modules. Each piece below links to the next, so a control you implement once shows up everywhere it's needed.
Frameworks
Adopt ISO 27001, SOC 2, PCI DSS, GDPR-style regimes and more, each tracked with a live compliance percentage.
Requirements
Every framework breaks down into the individual rules you have to satisfy — one master checklist, not a dozen spreadsheets.
Controls
Implement a safeguard once and it counts toward every framework that needs it, instead of re-proving the same thing repeatedly.
Evidence
Upload proof, route it through a review lifecycle, and get ahead of expiring evidence before an auditor finds it first.
Risk register
Score risks by likelihood and impact, track inherent vs. residual risk, and assign treatment plans with owners and due dates.
Audit readiness
One composite score rolls up requirements, evidence, and open findings — then bundle everything an auditor needs in one click.
Audit trail
Every write is logged automatically and can never be edited or deleted — a real, append-only record for external auditors.
Vendor risk
Track third parties, their DPAs, and their risk tier alongside your own posture, without a separate tool.
See your first framework tracked by end of day
No setup call required — adopt a framework and the checklist builds itself.
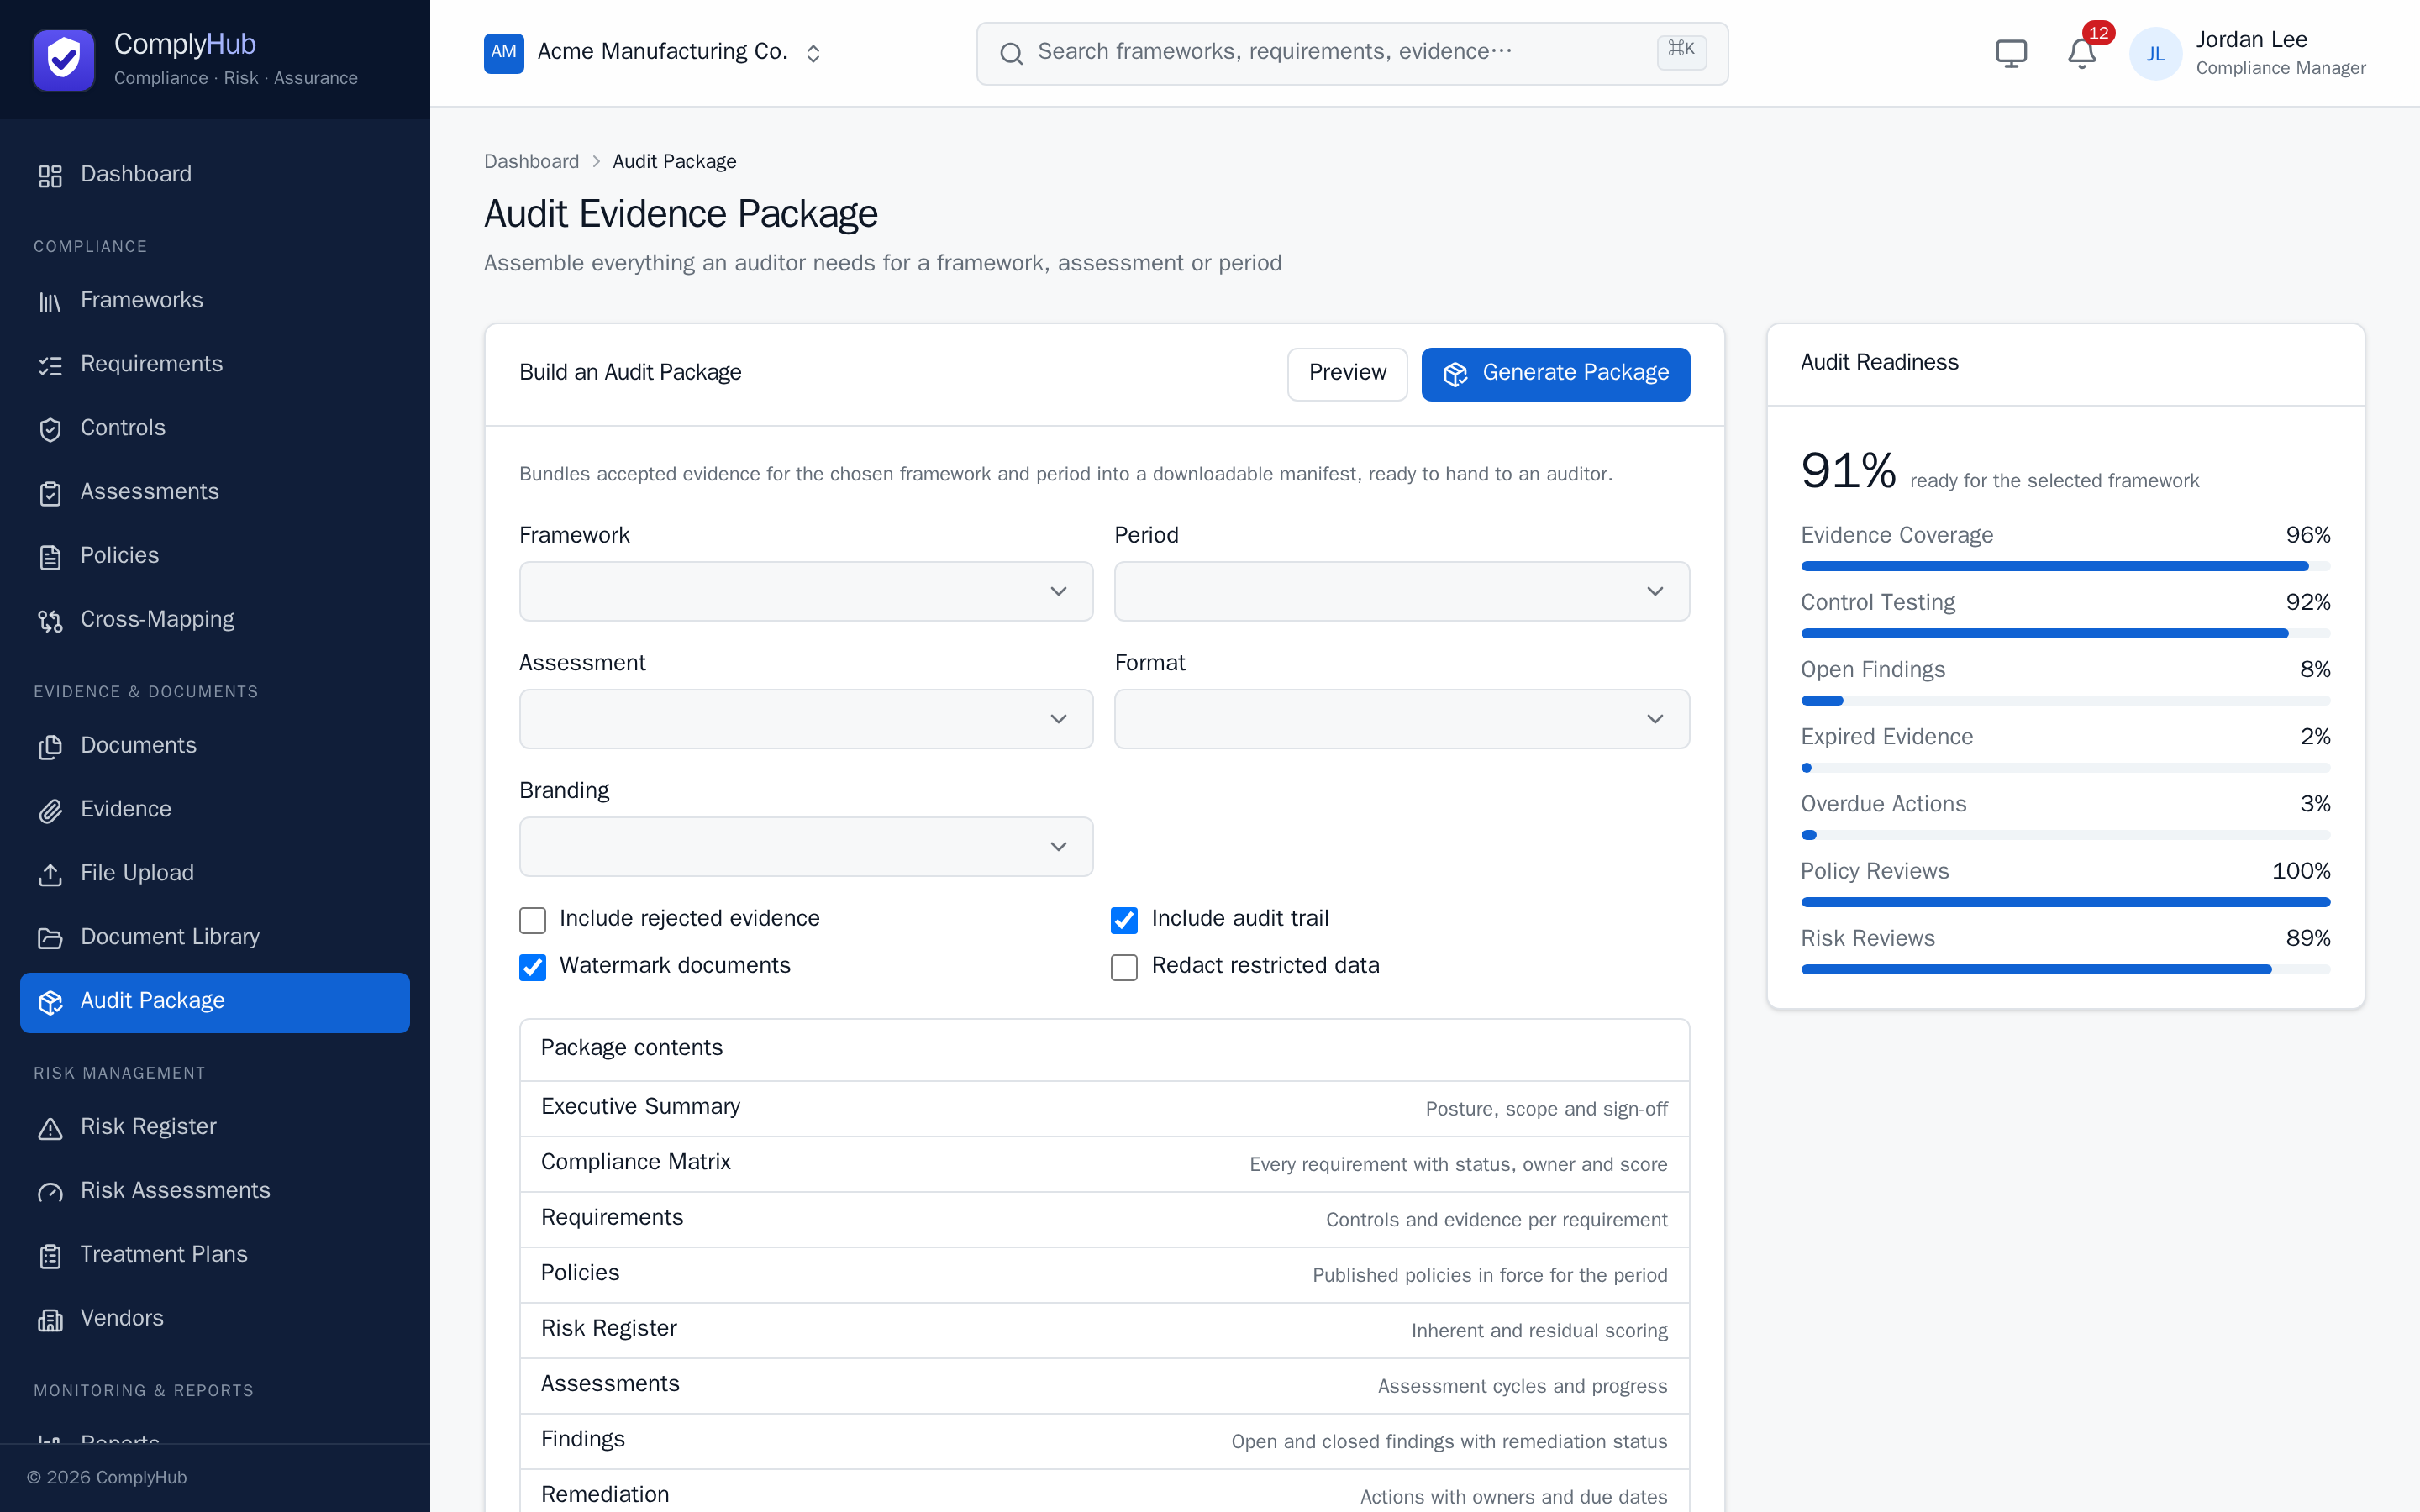
Audit readiness
Know your number before an auditor asks for it
Evidence coverage, control testing, open findings, expired evidence, overdue actions, policy and risk reviews — all rolled into one readiness score. When it's high enough, bundle everything into a single package an external auditor can work from directly.
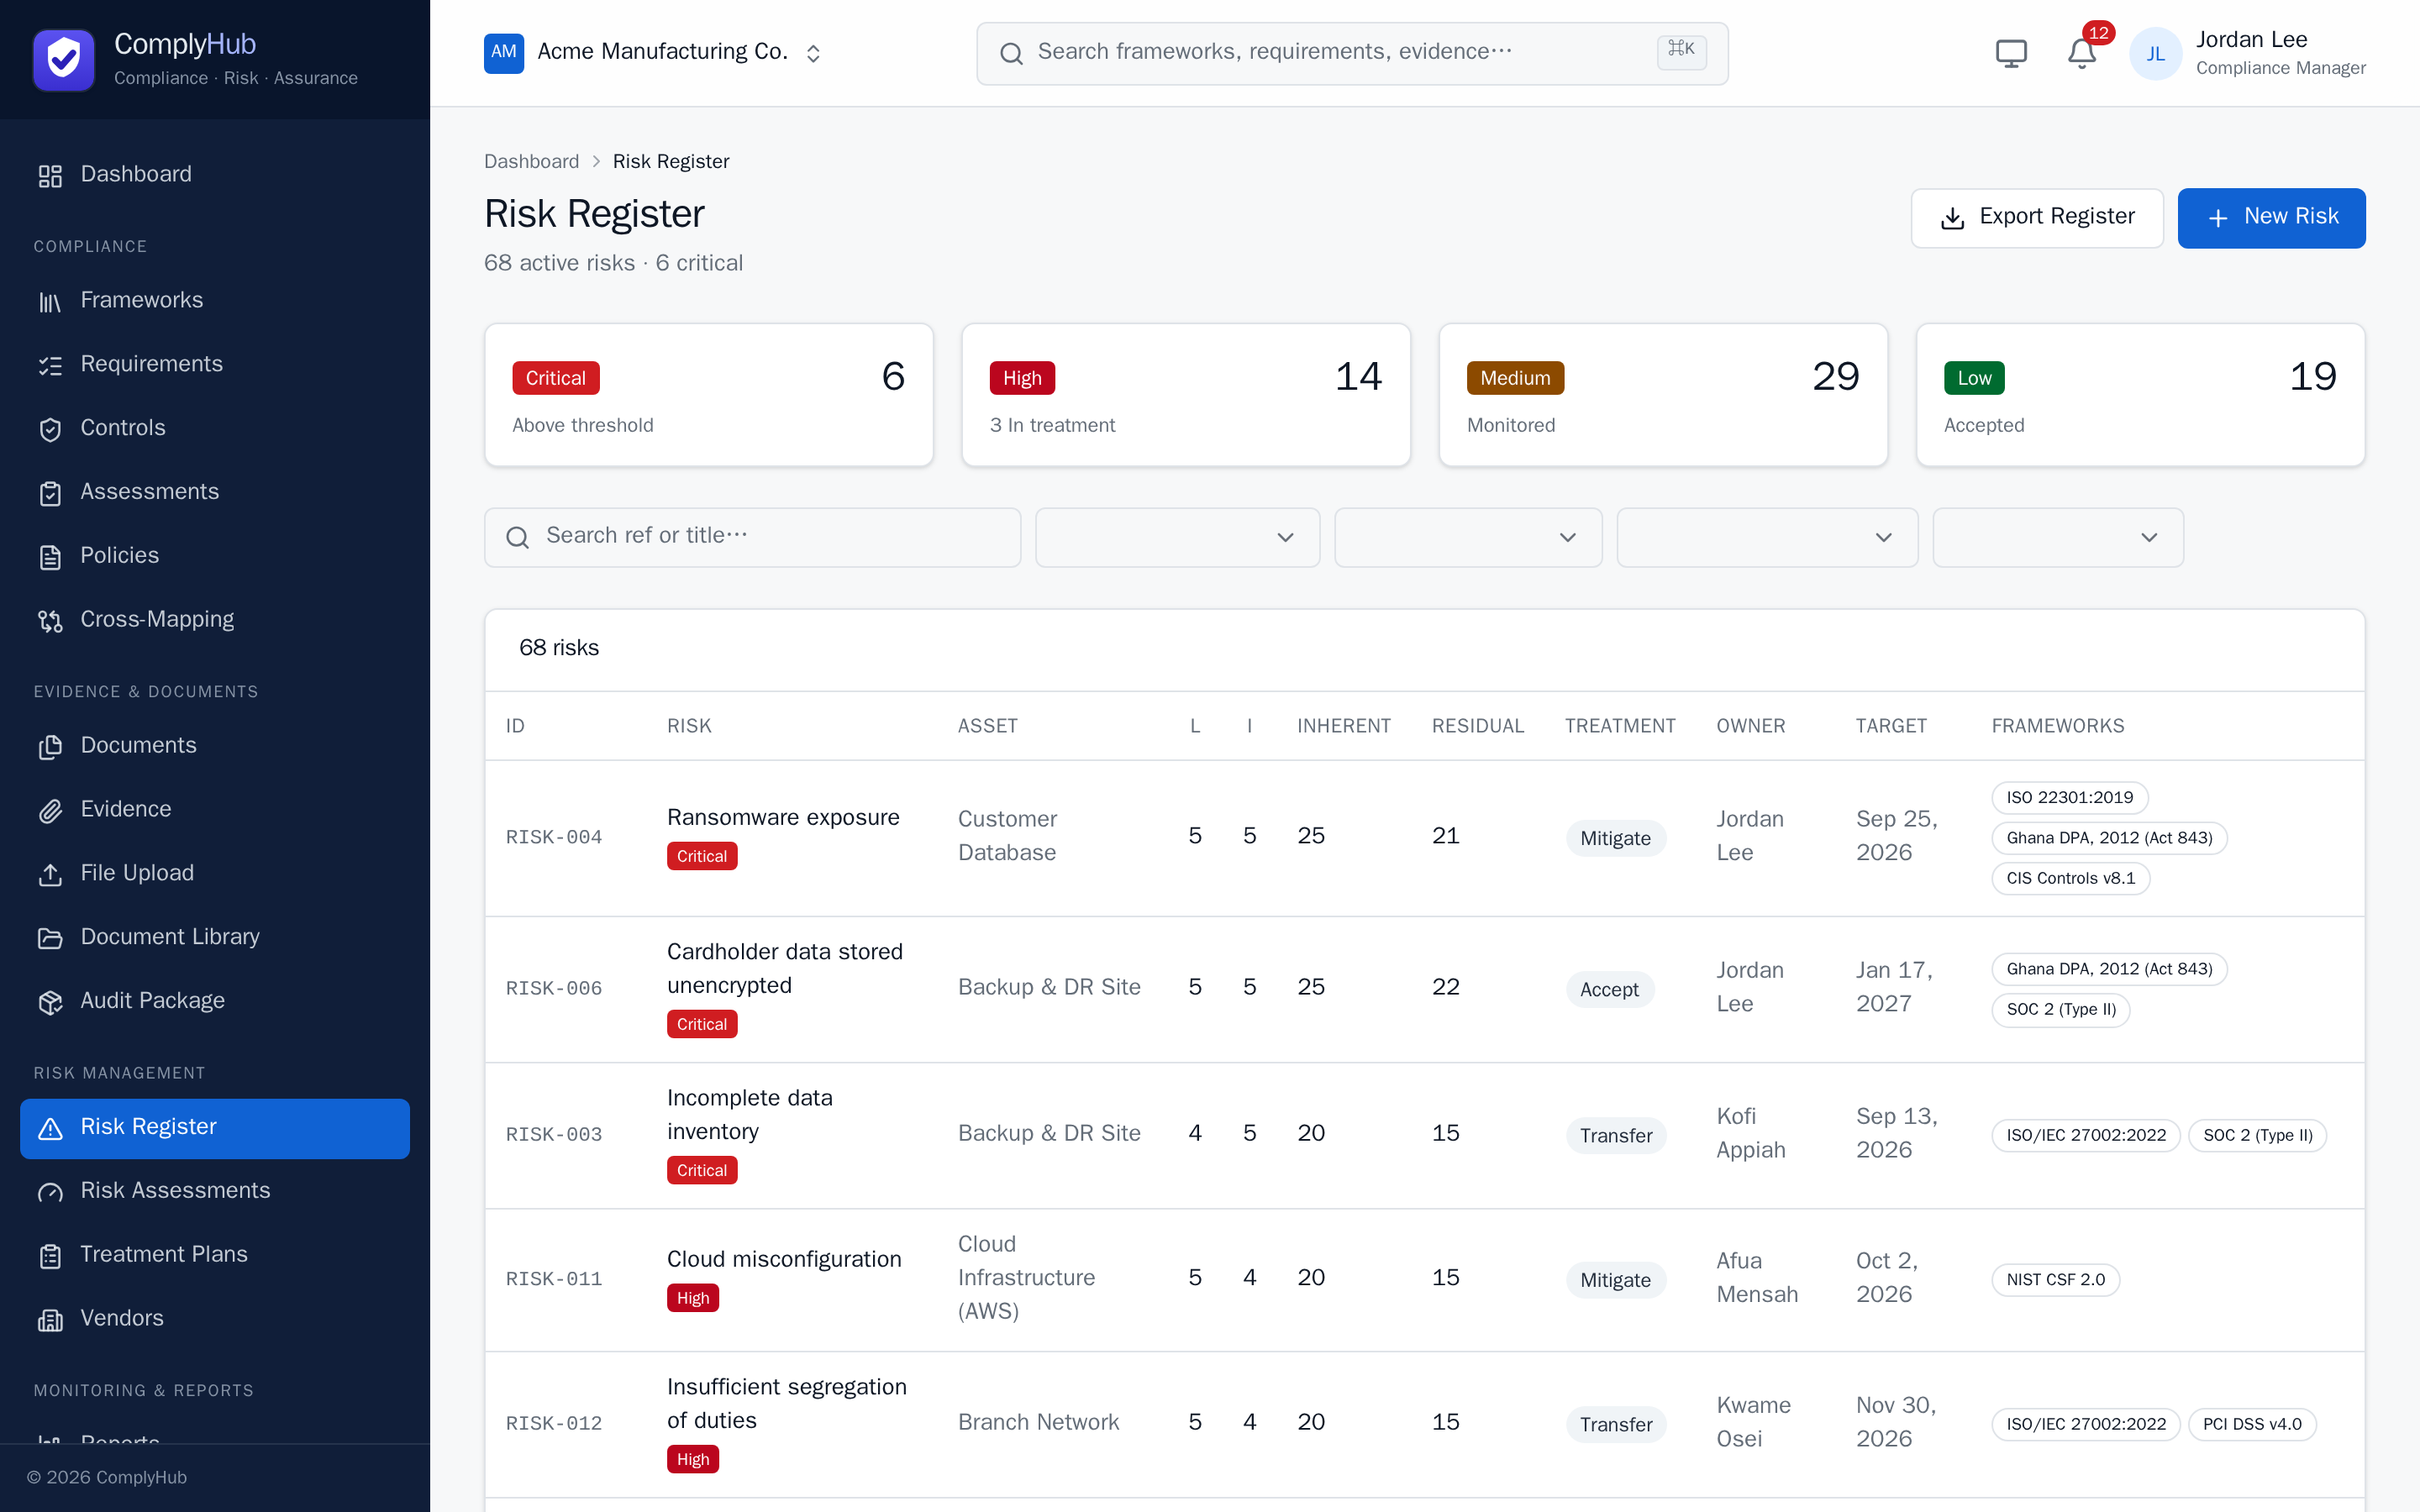
Risk register
Inherent risk vs. residual risk, side by side
Score risks by likelihood and impact, see exactly how much your controls and treatment plans actually reduce them, and assign a treatment strategy — mitigate, accept, transfer, or avoid — with an owner and a target date.
Who it's for
Sized for a lean team, built for a large one
The same platform scales from a five-person startup's first framework to a multi-org enterprise program.
Small & mid-size teams
Move fast on your first framework without a dedicated compliance hire.
- Get a first framework tracked and audit-ready without hiring a compliance team
- Guided onboarding tour walks new users through the whole workflow
- Pay for what a lean team actually needs — start with one framework, one org
Enterprises
Multiple business units, strict access control, and a real integration surface.
- Multiple organizations and workspaces under one account, each independently scoped
- Role-based access control, SSO via OIDC, and mandatory MFA policy enforcement
- A documented REST API (with scoped API keys) for wiring into existing tooling
- Full audit trail and access reviews for internal and external auditors alike
Choose your path
Built for teams with a compliance lead, and teams without one
Both run on the same hosted platform — pick the level of hands-on help that matches your team.
For teams without dedicated compliance staff
If nobody on your team has done this before, ours works directly with yours: configuring frameworks, importing existing evidence, and setting up roles and SSO so you're not starting from a blank screen.
Talk to our teamFor teams who want to drive
If you already know your frameworks and just need the tooling, sign up and configure everything yourself — frameworks, controls, evidence, roles. Support is there if you need it, but nothing requires a call.
Start self-serve